
Reference architecture
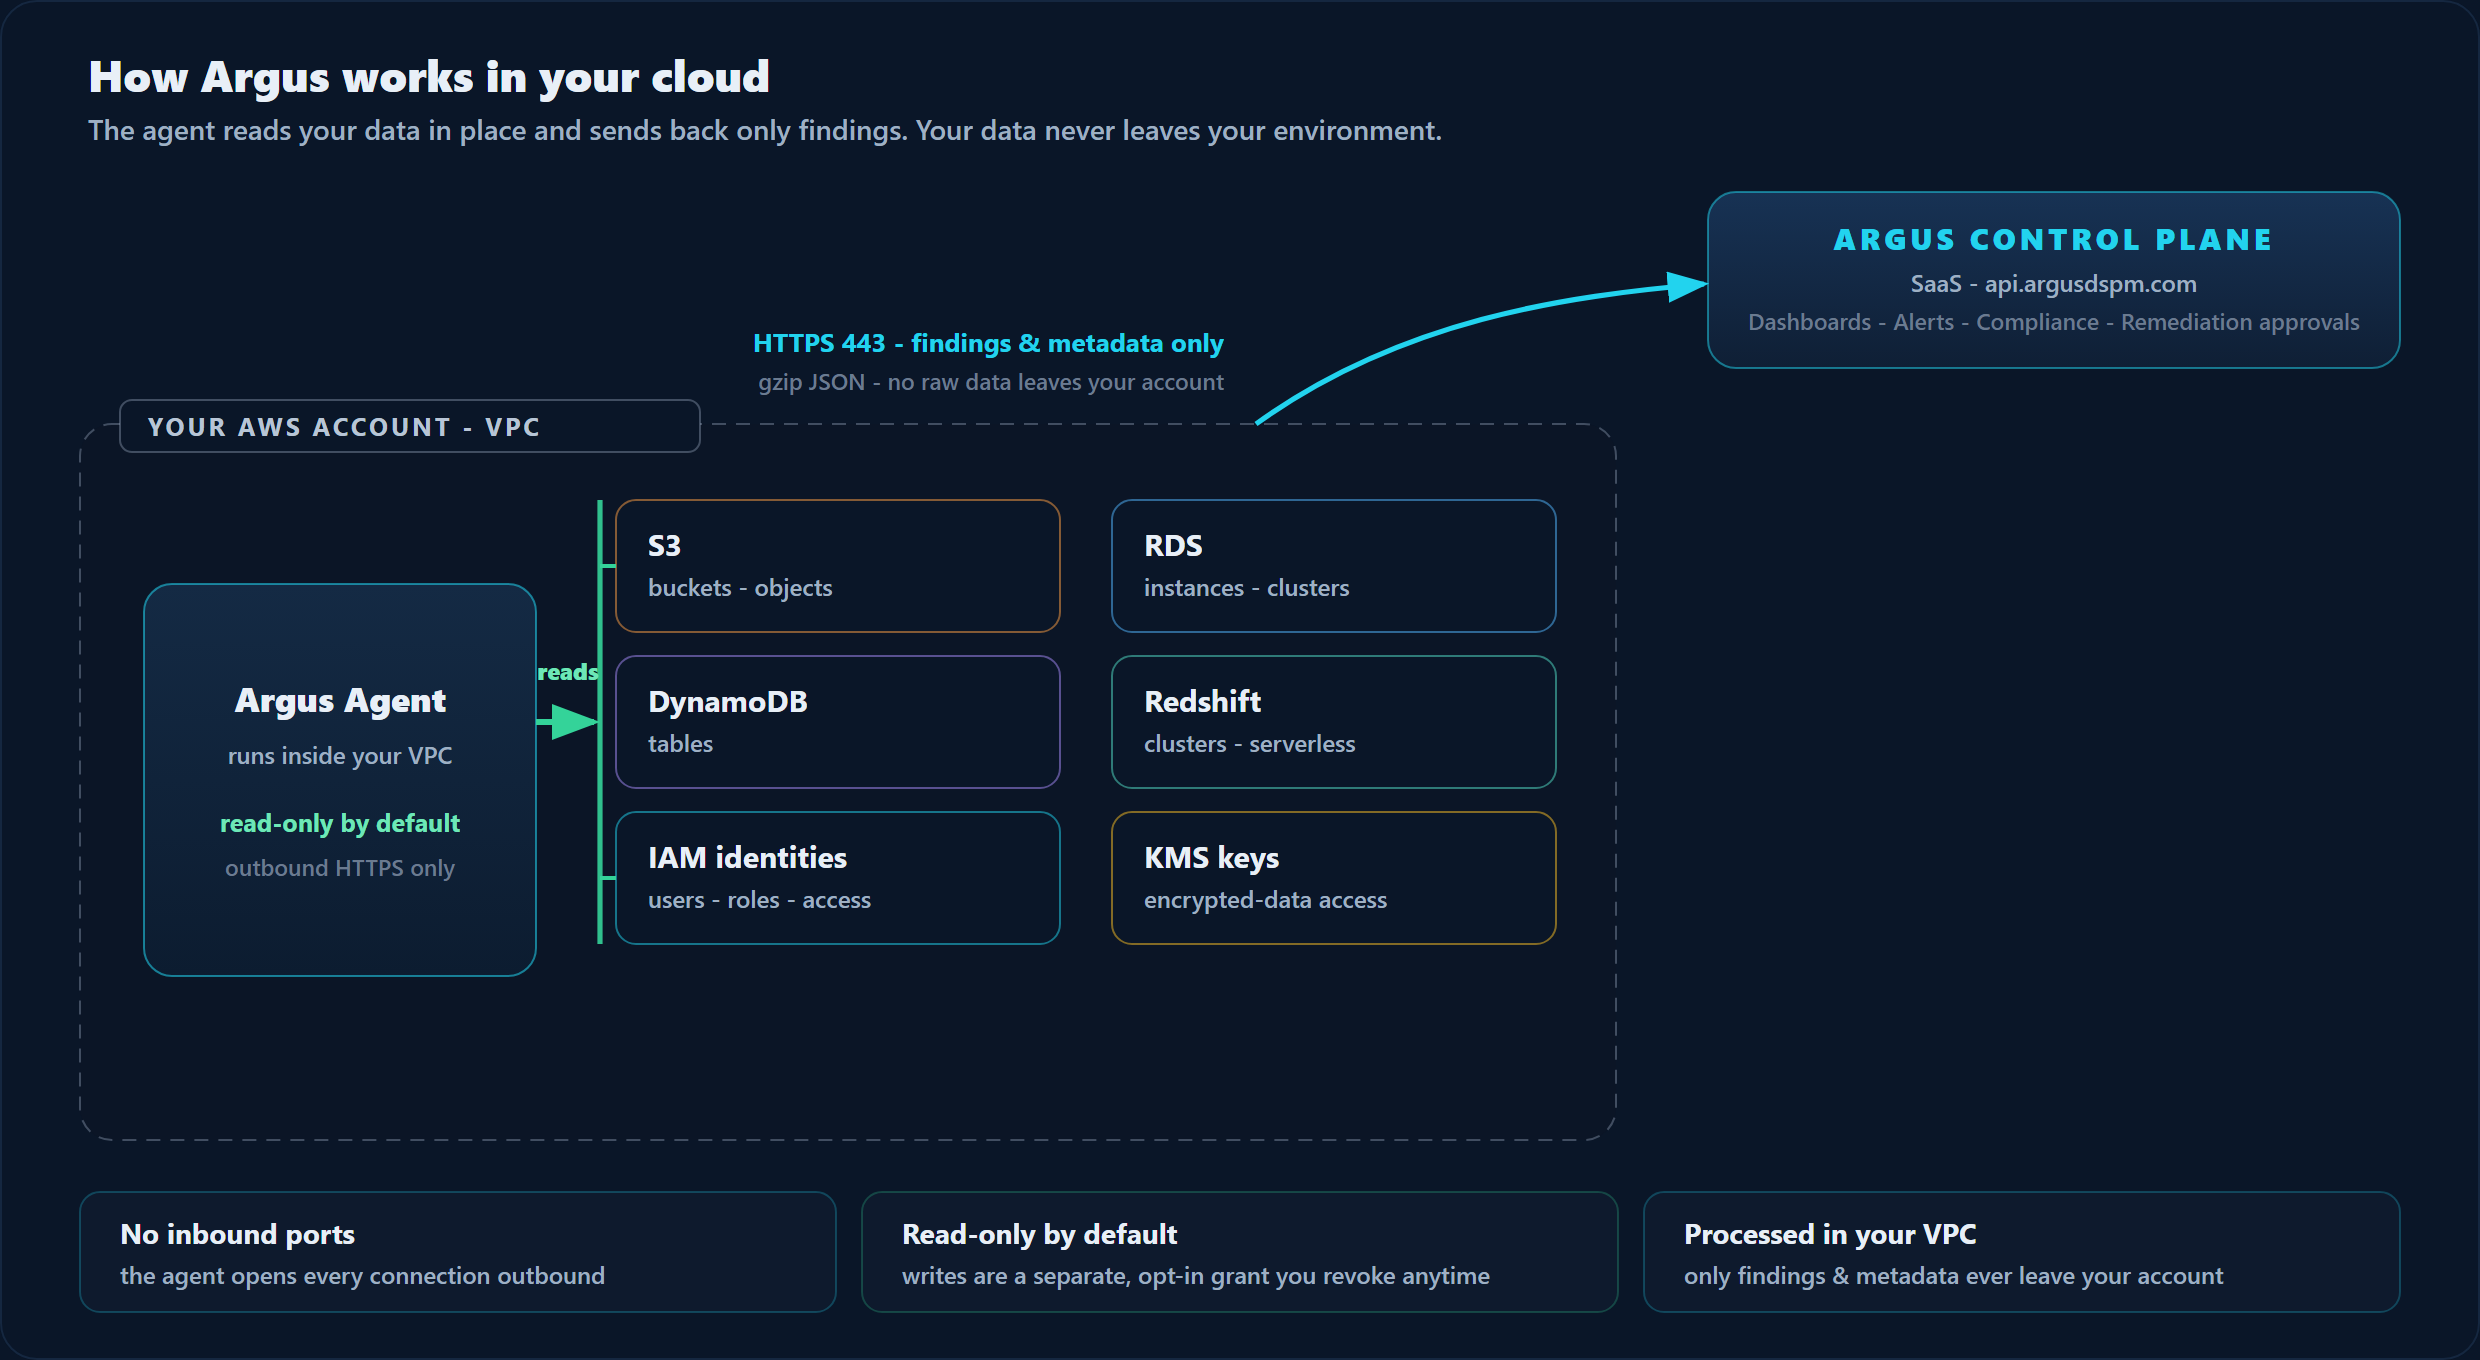
The Architecture page explains the split control-plane / data-plane design in prose. This page shows it. Both diagrams are AWS reference architectures (the EC2 variant runs a single instance in place of the Fargate service; everything else is the same).
How it works
Section titled “How it works”The agent runs inside your VPC, reads your data in place, and sends back only findings. Your data never leaves your environment.
In-account footprint
Section titled “In-account footprint”Everything the CloudFormation stack creates (left, all argus-prefixed) and everything the agent reads (right, your existing resources). Reads are the default; writes are a separate, opt-in grant that is off unless you enable remediation.
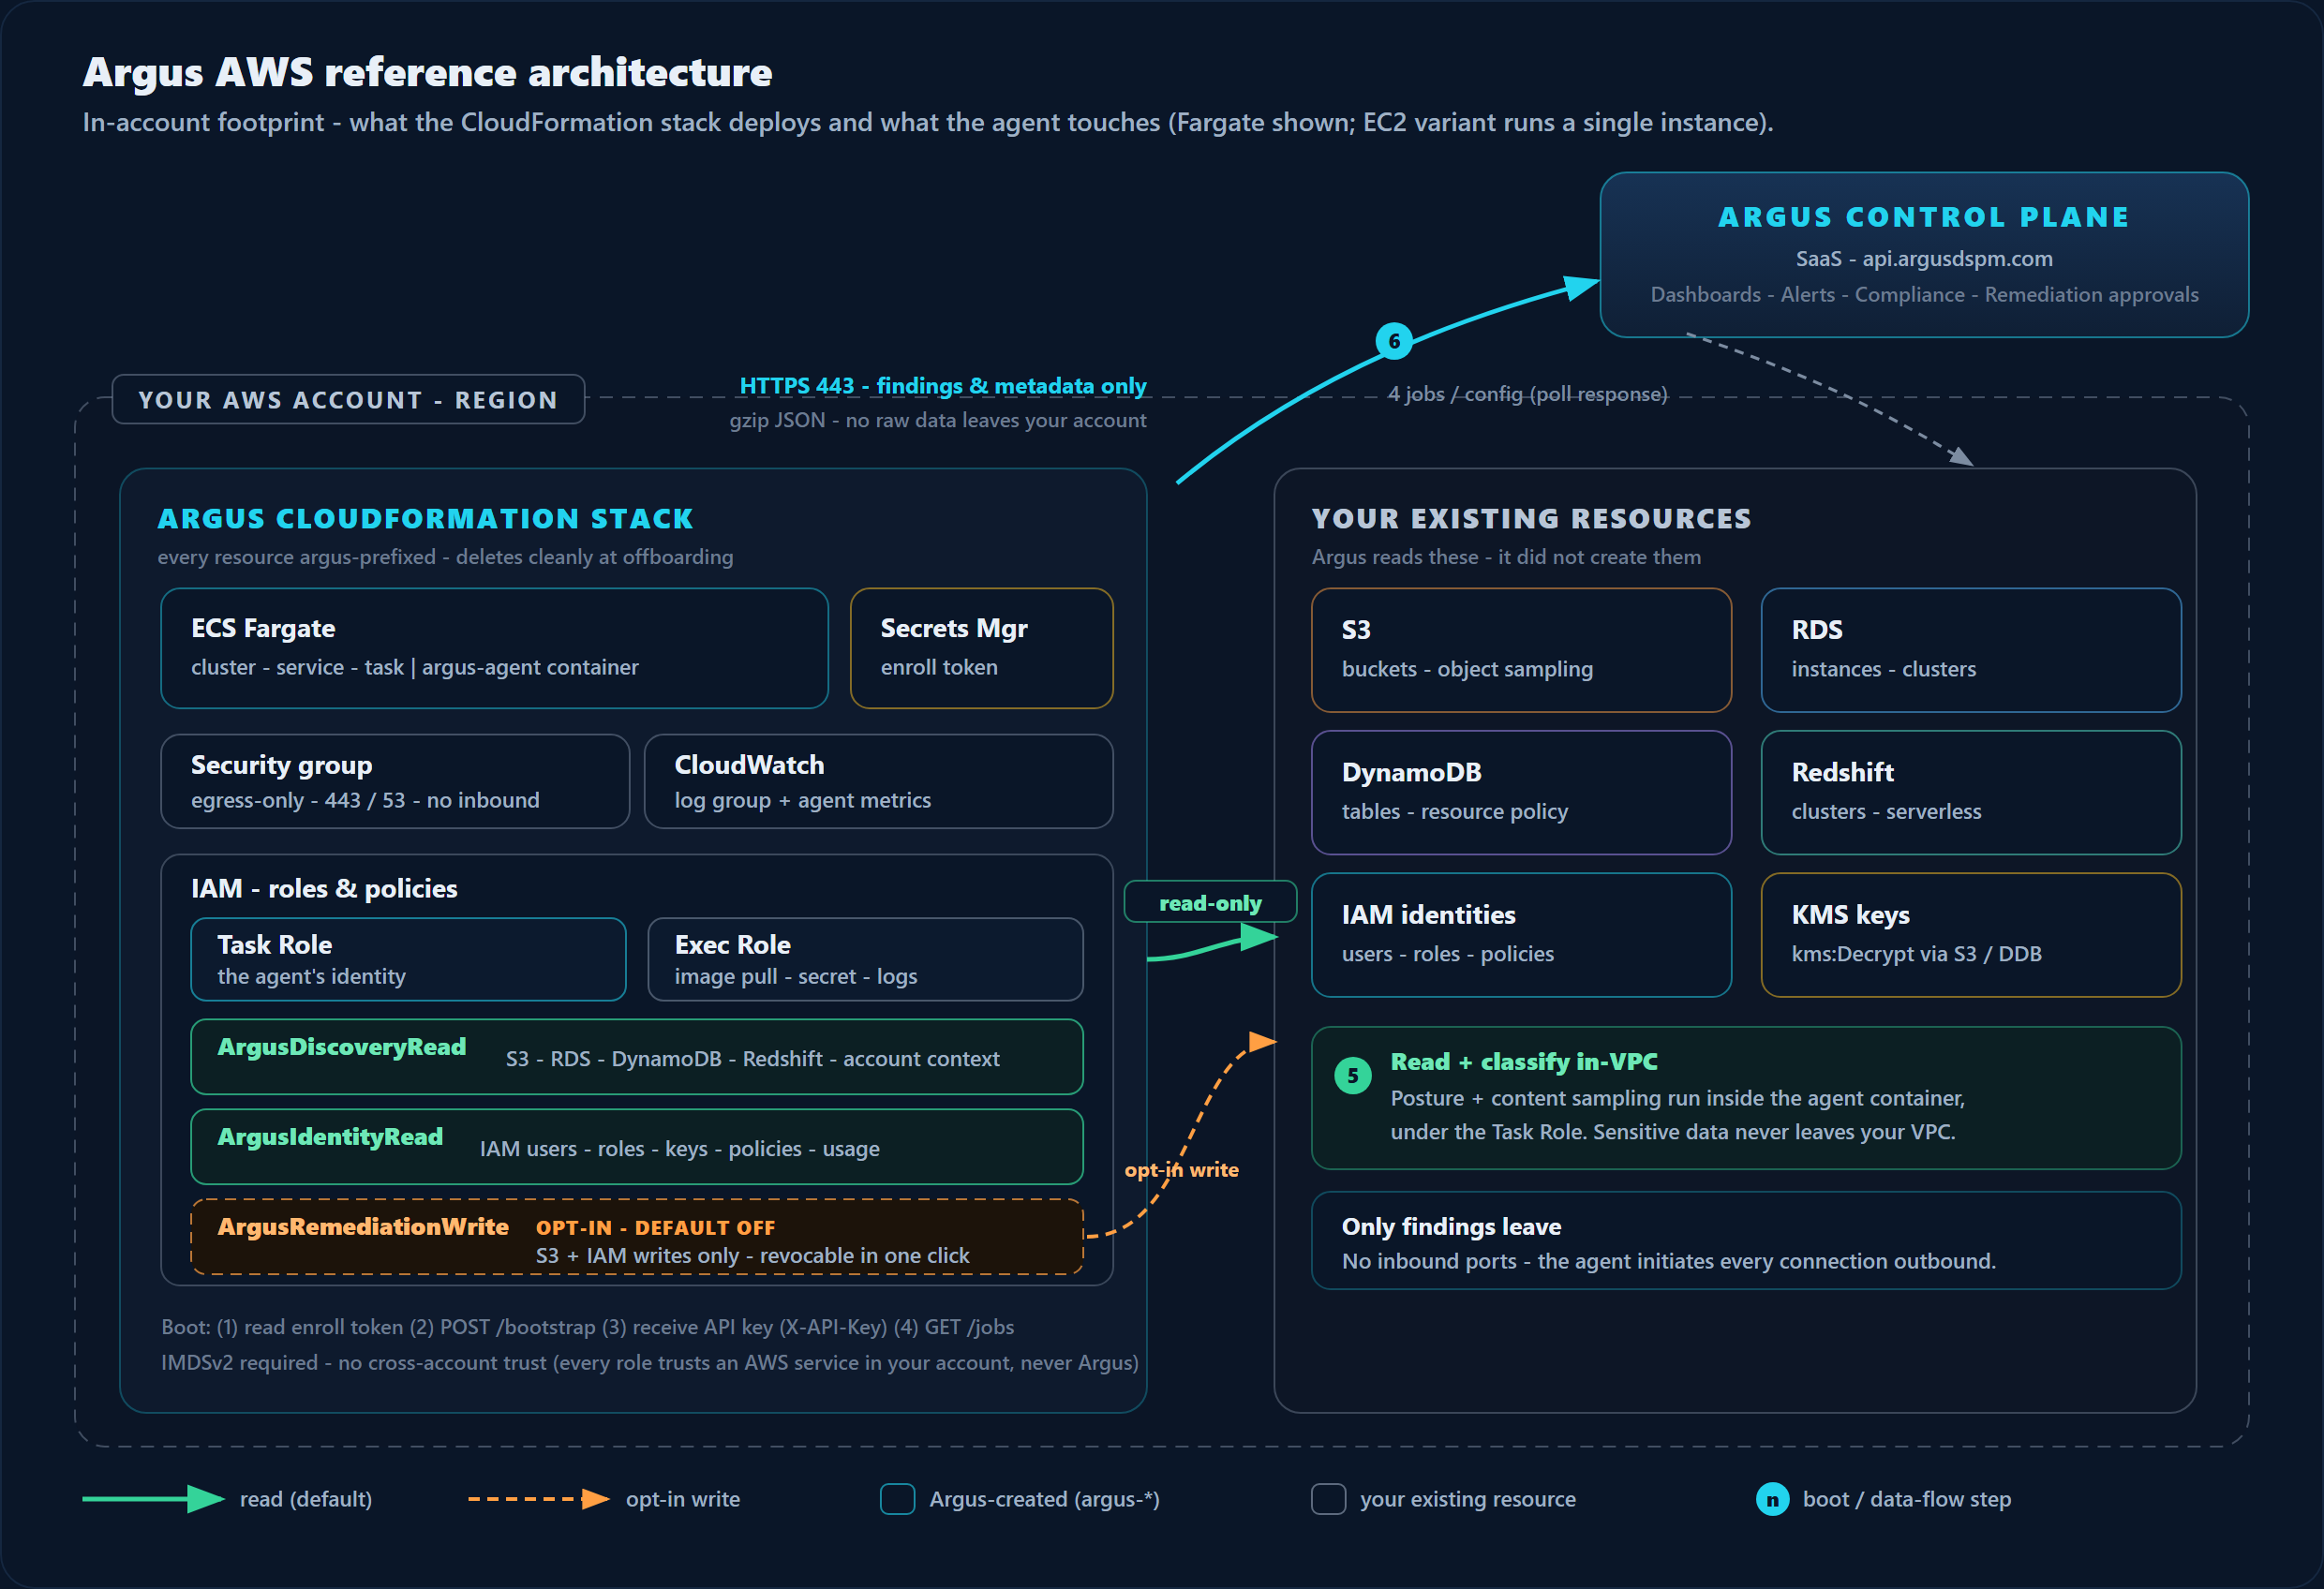
For the exact IAM statements behind the read and opt-in-write policies, see IAM permissions. For what the stack creates per deploy shape, see Deploy overview.
Download
Section titled “Download”For sharing outside the docs (a security review, a follow-up email) - PNG for a quick drop-in, SVG to scale, PDF for both on printable pages:
- Boundary diagram: PNG · SVG
- Footprint diagram: PNG · SVG
- Both diagrams (PDF)